Know where you stand. Be able to show it.
CyberAssure is how we measure how ready your business is to take a hit and recover from it. You get a Cyber Readiness score across eight areas, the evidence behind every part of it, and a plan for the gaps. It gets you ready for the audit. It doesn’t replace the auditor.
The score
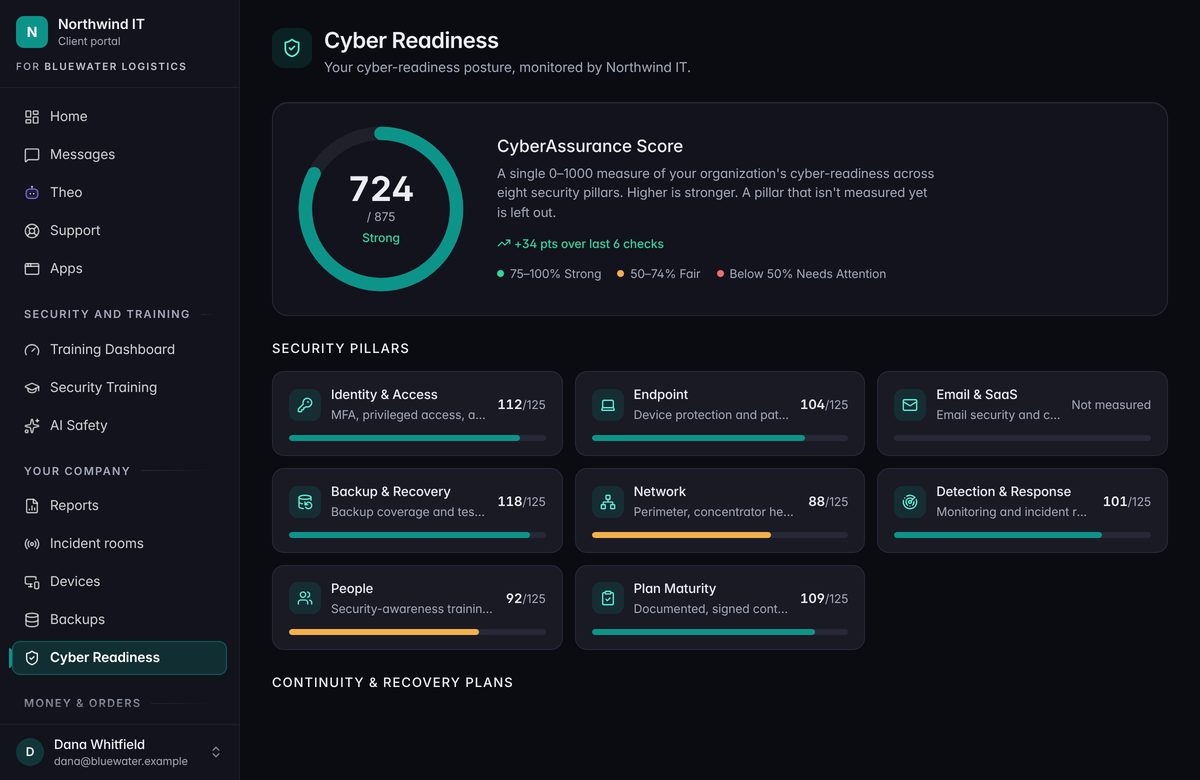
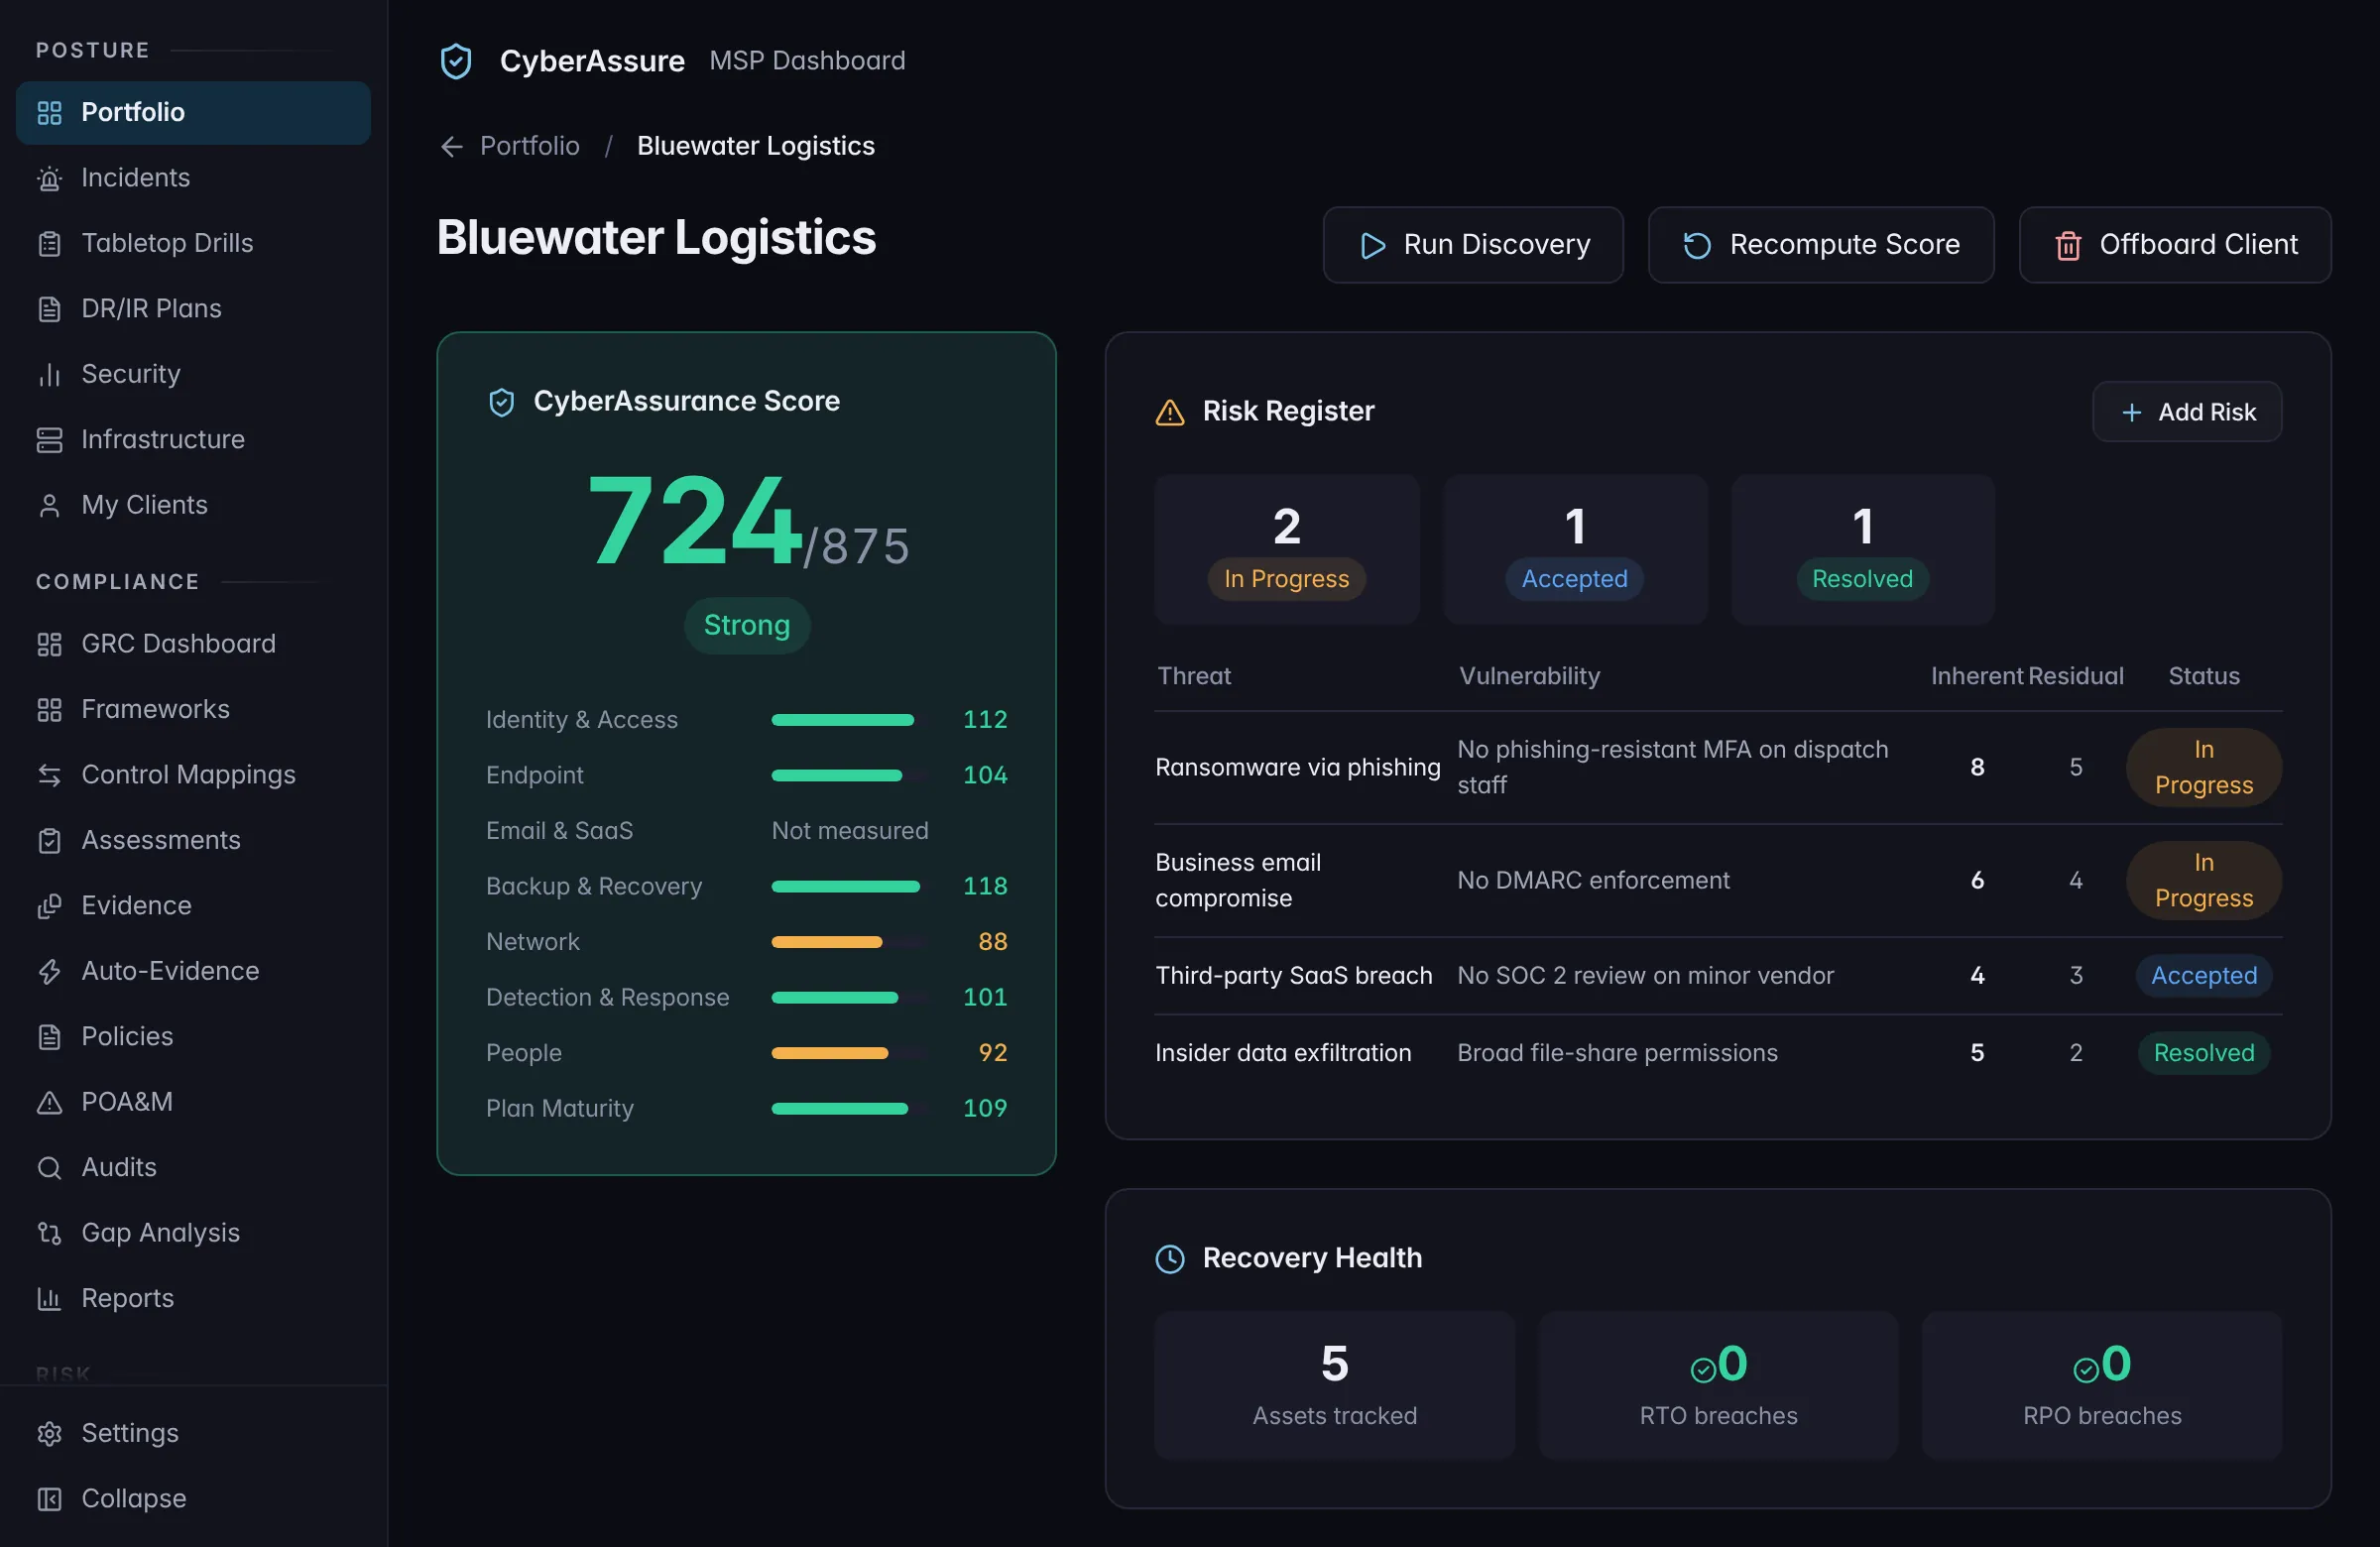
Eight areas. One honest number.
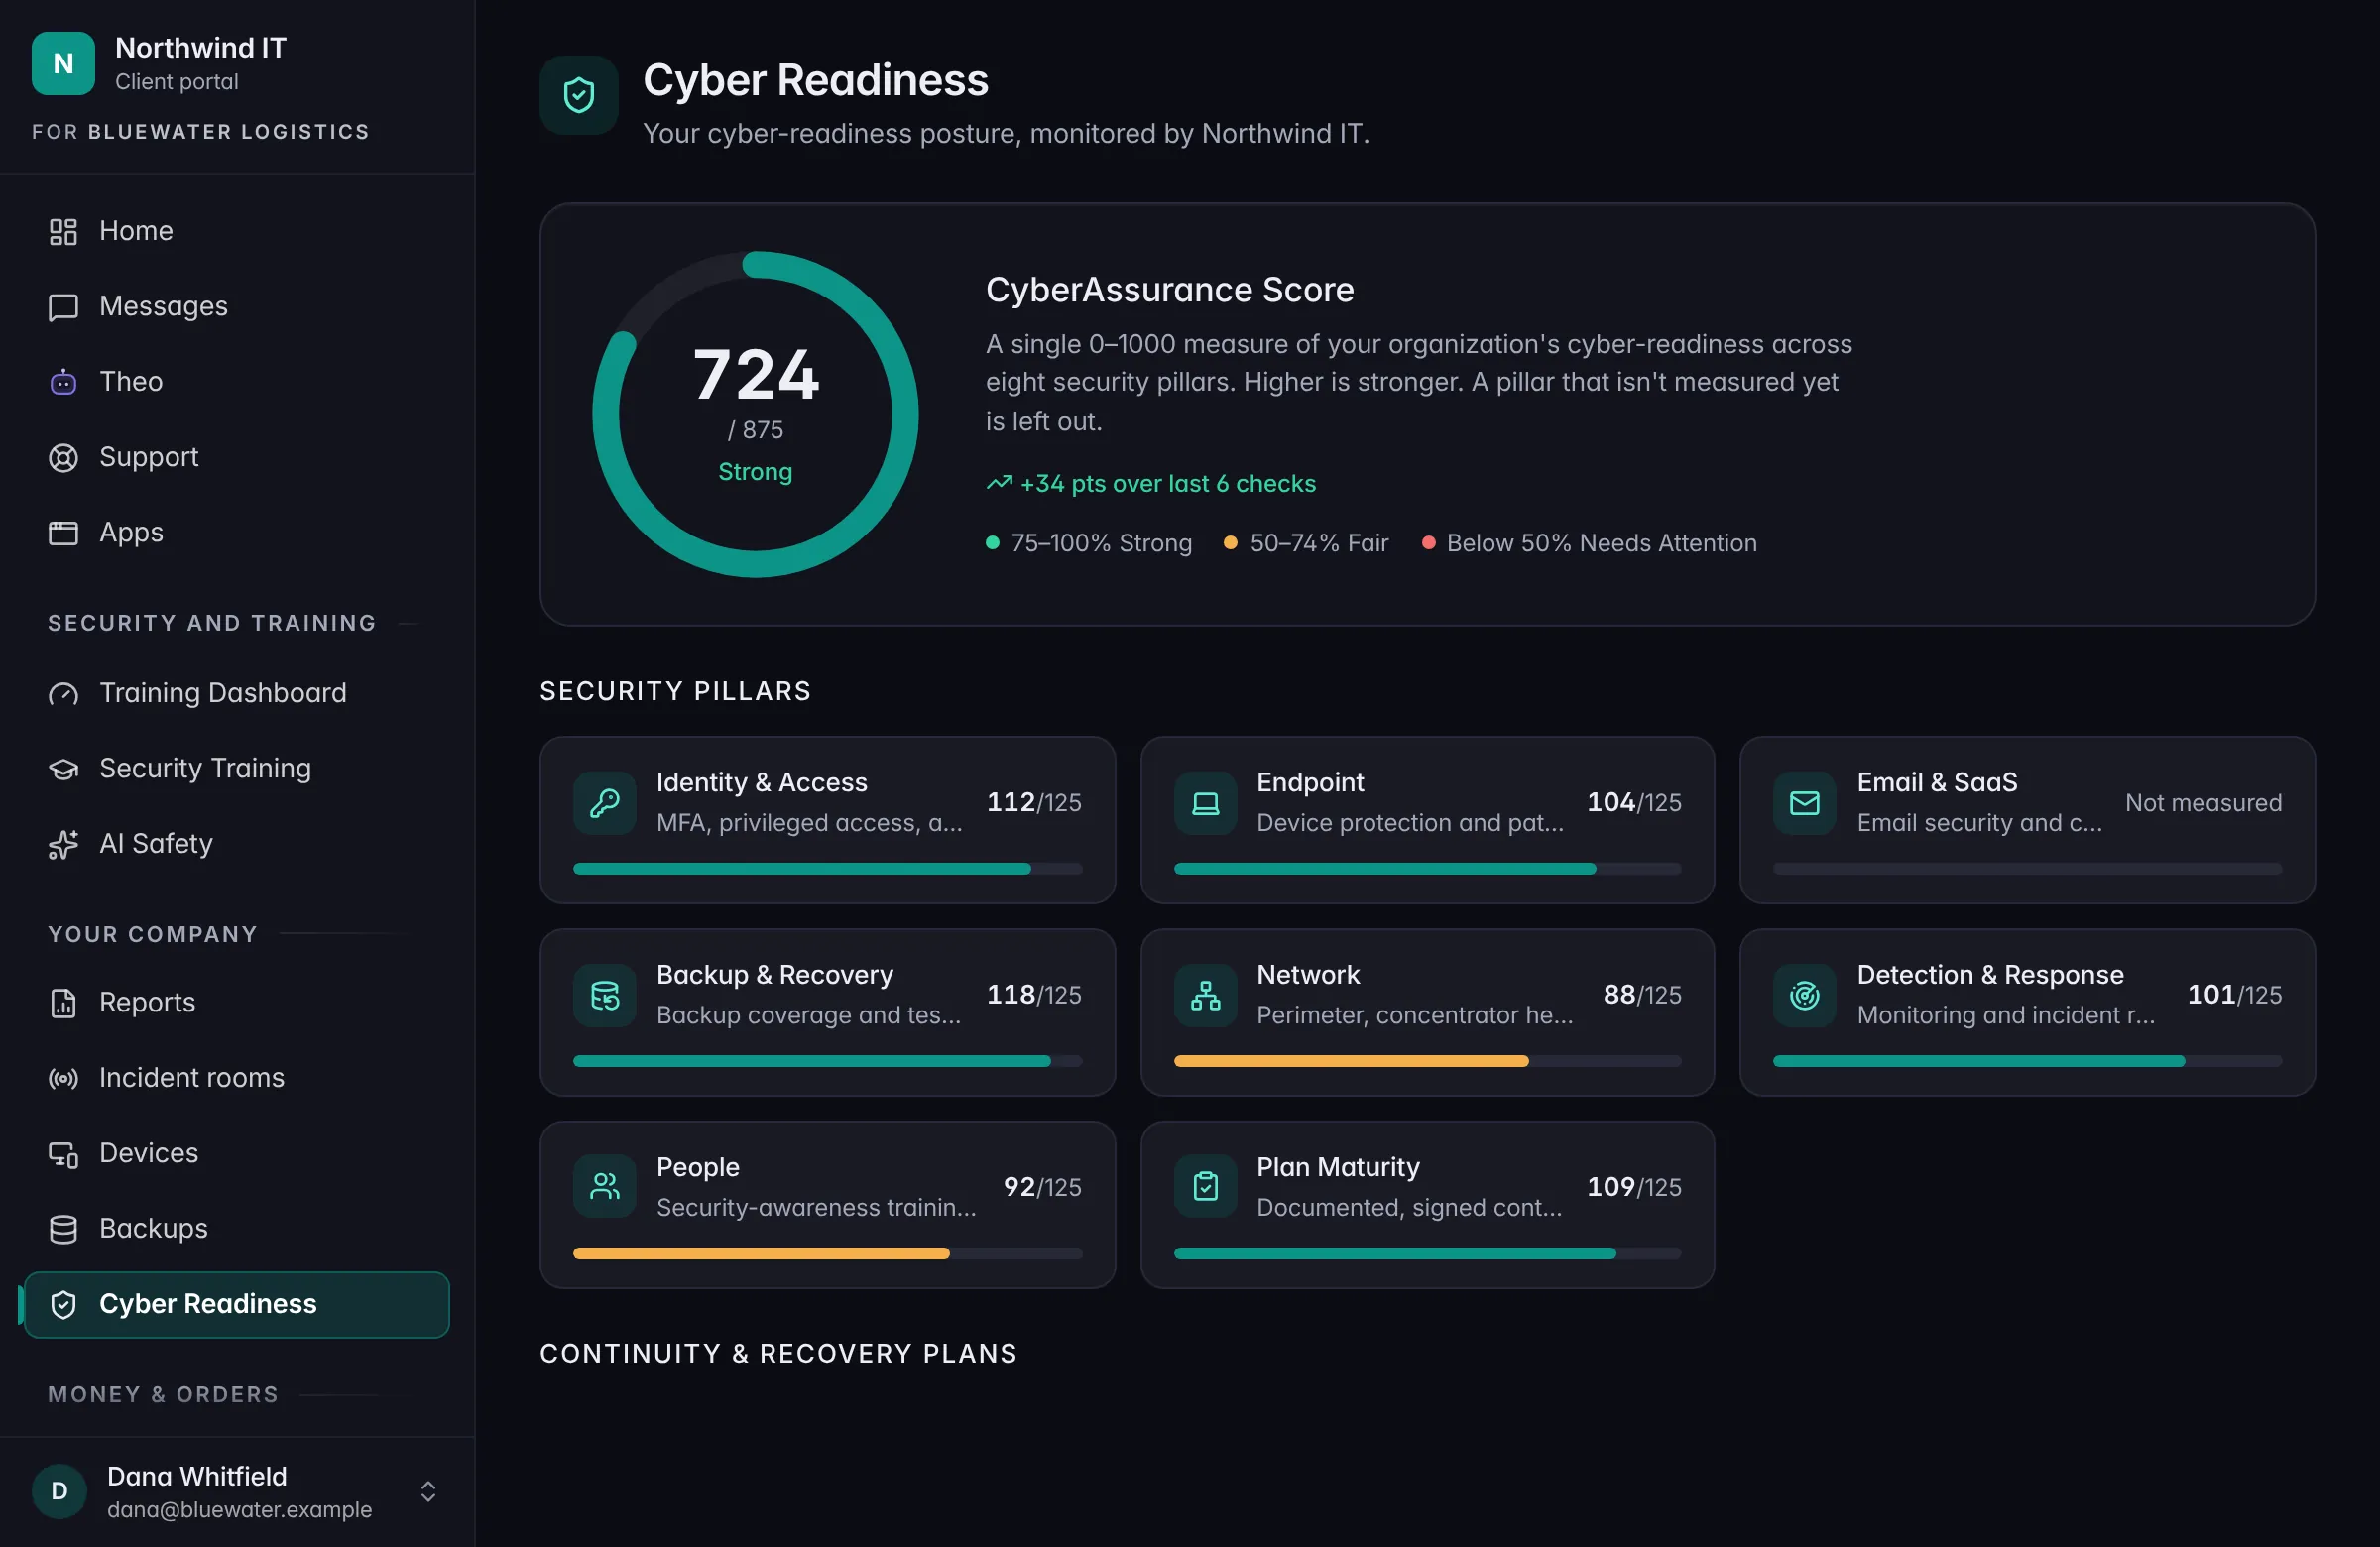
Security isn’t one thing, so the score isn’t either. It’s built from eight areas, and you can see which ones are carrying you and which ones aren’t.
Identity
Sign-in protection, admin accounts, and accounts that should have been closed.
Devices
Whether every computer is protected and up to date.
Email and apps
How your email and your cloud apps are locked down.
Backup
What’s backed up, and whether a restore has been tested.
Network
The edge of your network, and how current its rules are.
Detection and response
Whether trouble would be noticed, and how ready the response is.
People
Security training, how people are keeping up with it, and cover for key people.
Plan maturity
Written, signed plans for staying open and for handling an incident.
If an area hasn’t been measured yet, it says “not measured”. It never shows as zero, and it never gets counted as fine.
Frameworks
Start from the standard you’re being asked about.
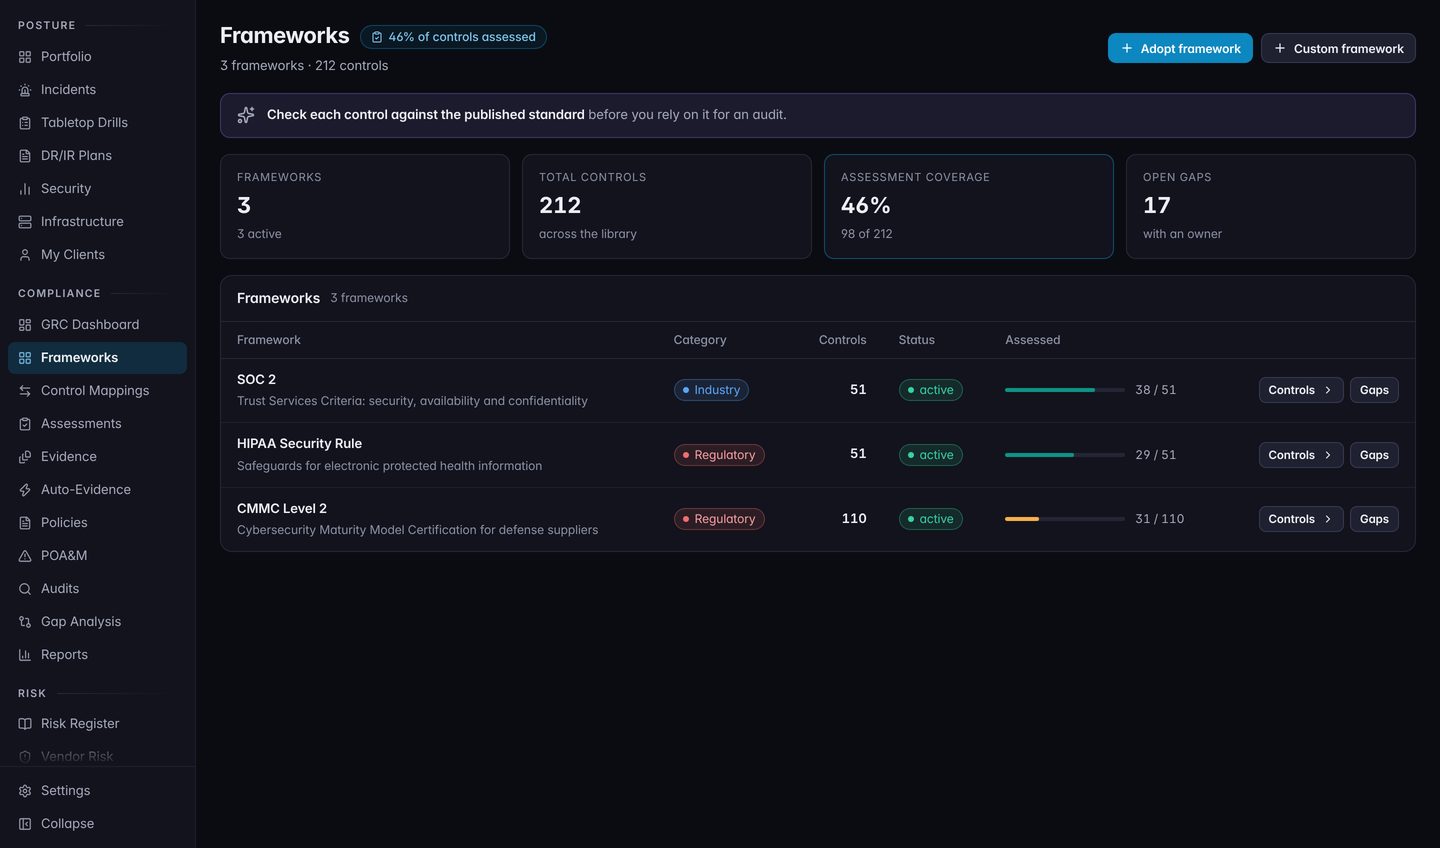
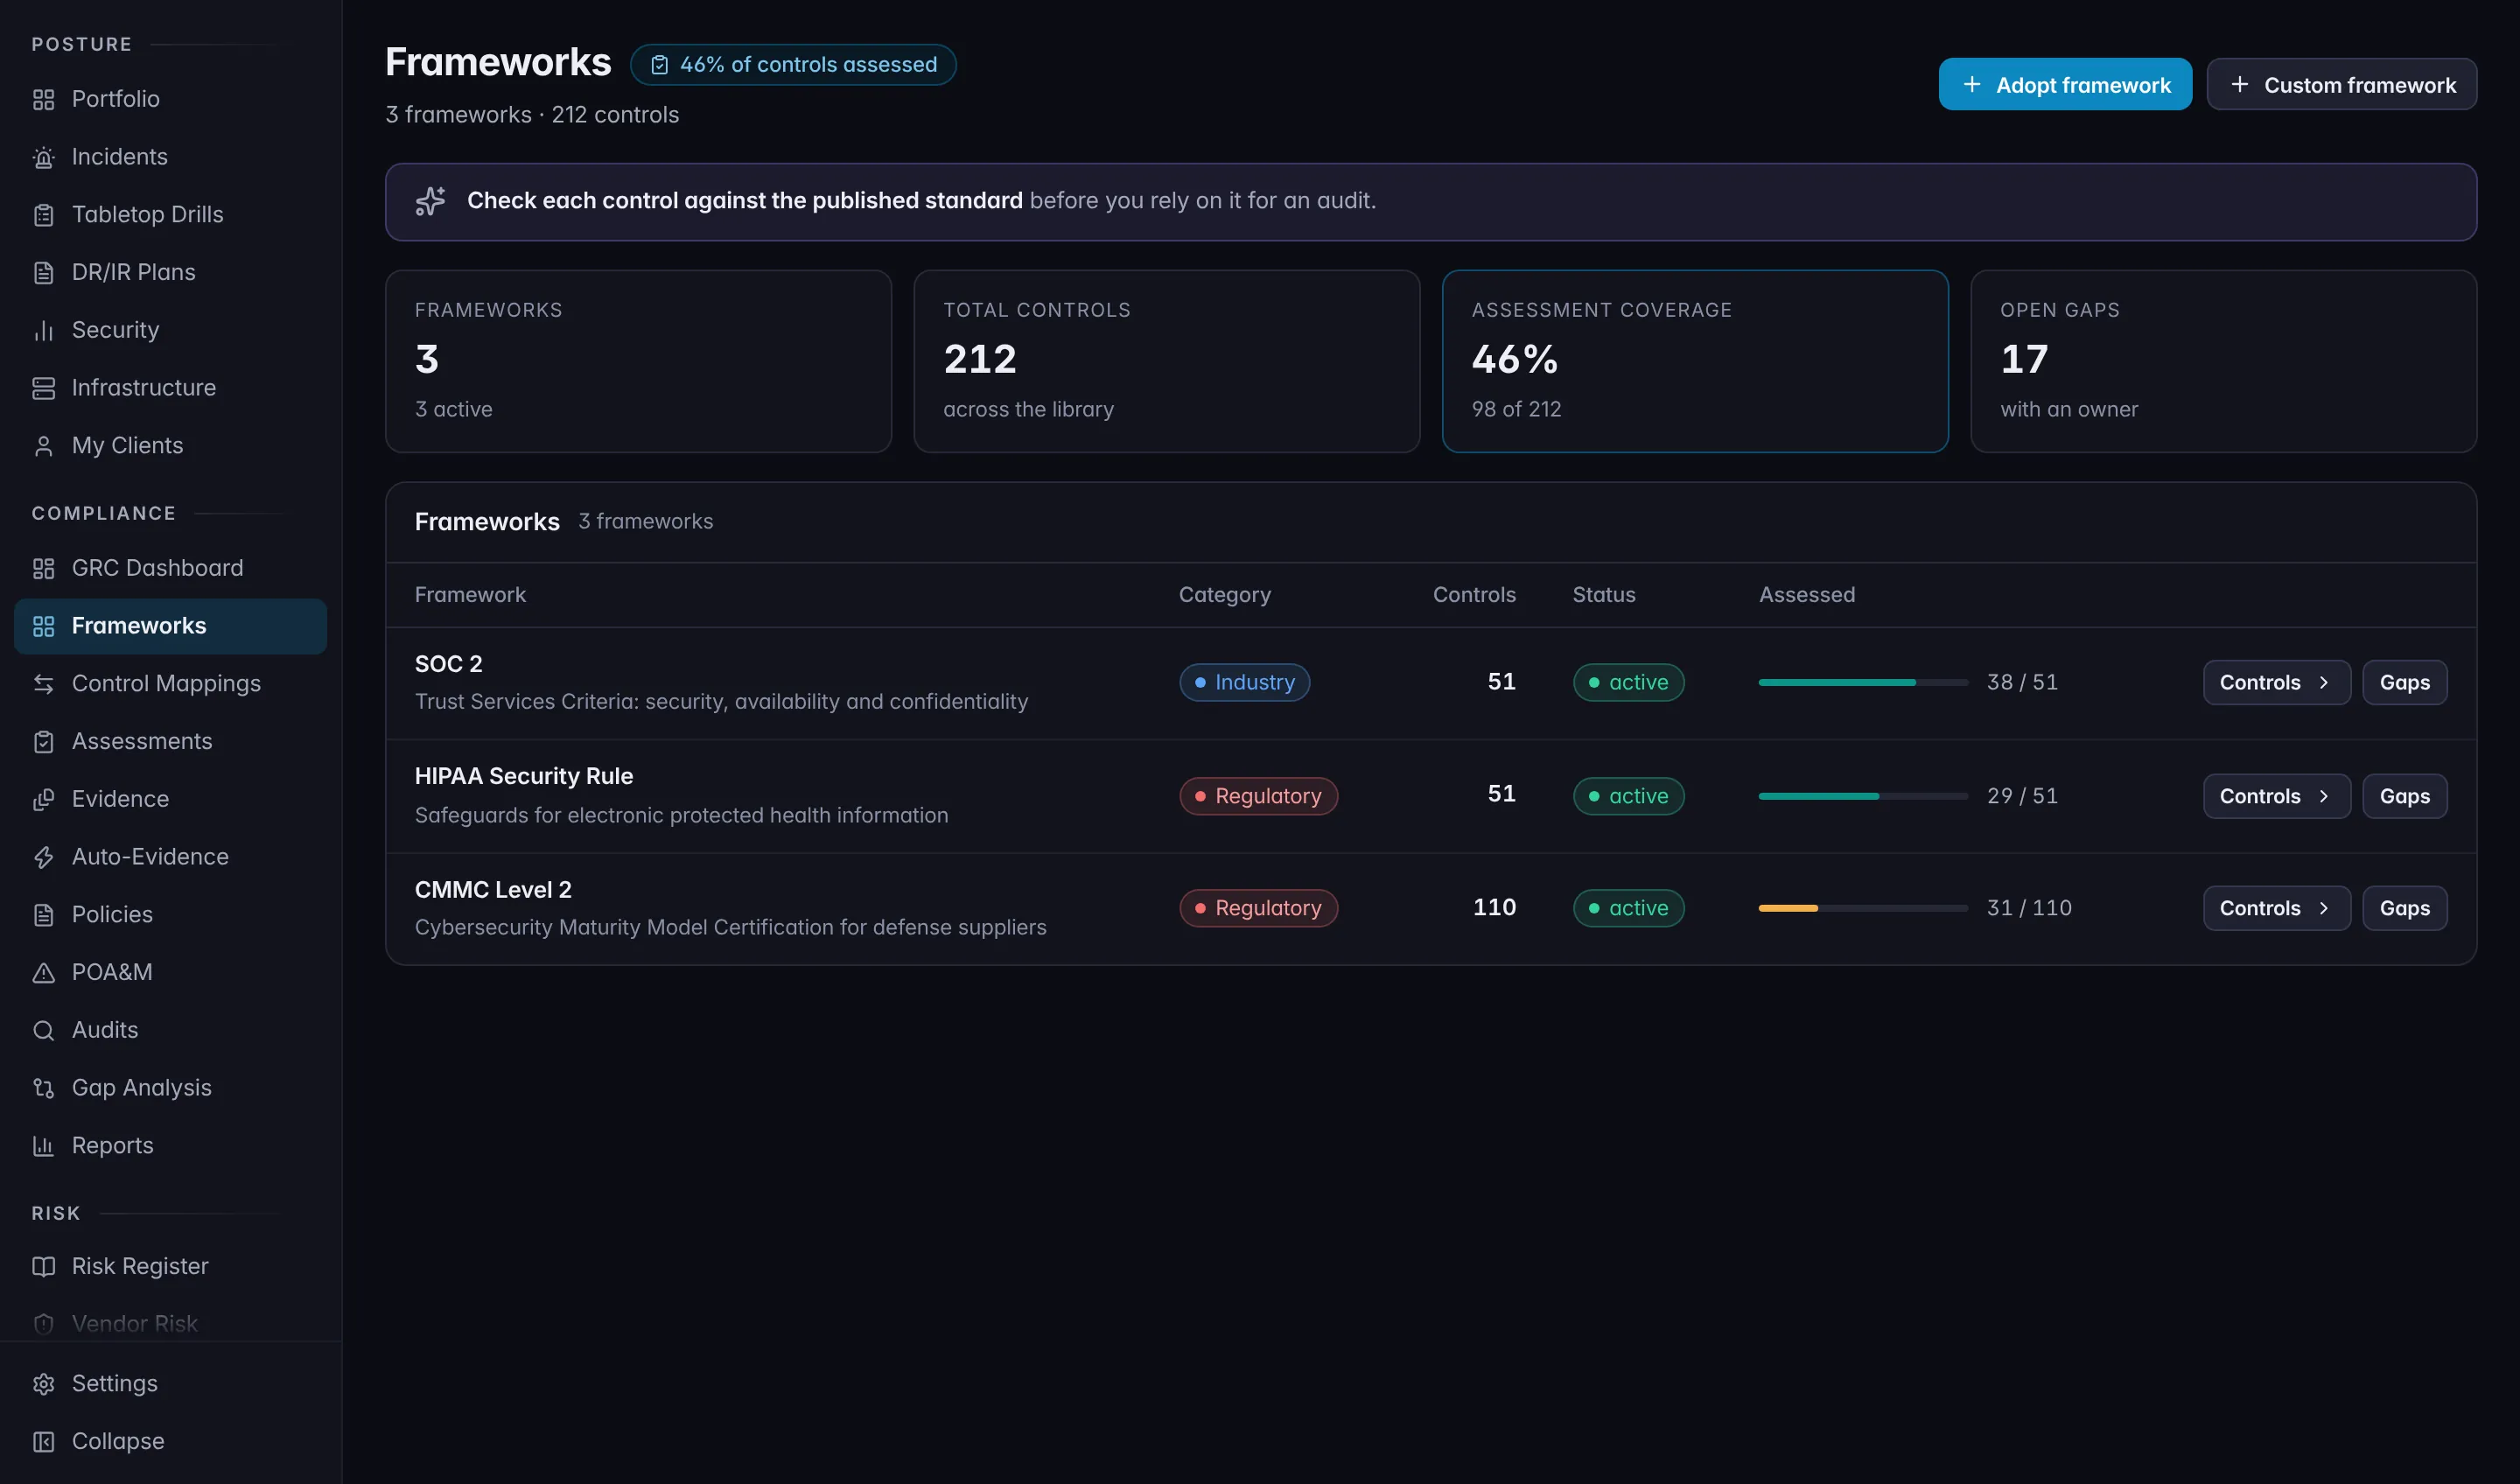
Each framework comes as a library of controls. We work from the ones that apply to you, and every control gets an owner, a status, and a date.
- SOC 2
- HIPAA
- PCI-DSS
- CIS
- NIST 800-171
- ISO 27001
- CMMC Level 2
A library is a working set of a standard’s controls, not the full published text. For a formal audit, the published standard is still the reference, and we check against it.
Not sure which one applies? That’s usually the first conversation, and it’s a short one.
What you get
The work behind the score.
A number by itself doesn’t satisfy an auditor, or a customer who sends you a security questionnaire. This does.
- Assessments
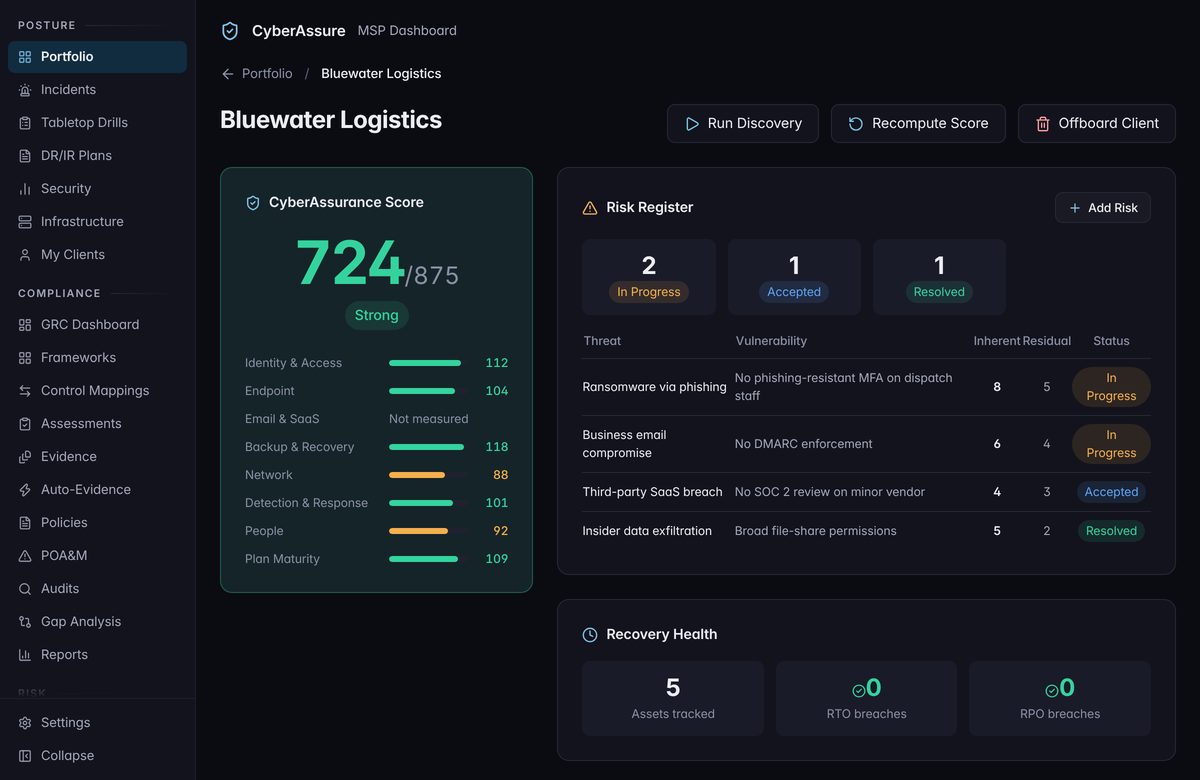
A review of your business against the framework you choose: where you meet it, where you don’t, and what nobody has checked yet. Our team runs it with you.
- Evidence
The proof behind each answer, kept in one place: policies, reports, screenshots, settings. Some of it can come from the tools we already run for you. Every item is reviewed and given an expiry date, so old proof doesn’t pass for current.
- Remediation plans
Every gap becomes an item with an owner and a due date, and we work the list with you.
- Vendor questionnaires
We send a security questionnaire to a vendor you depend on. They answer through a link, and the answers stay on file.
- Signed DR and IR plans
A disaster recovery plan and an incident response plan, written for your business. A plan counts as signed only when your owner and our people have all signed it, and it gets flagged when it’s going stale.
- Tabletop exercises
A practice run of a bad day: monthly, quarterly, or once a year. What everyone learned gets written up afterwards.
- Your Cyber Readiness view
A read-only page in your Client Portal with your score, where each area stands, your plans, and how much evidence is on file.
- Audit-ready packages
When an auditor or an assessor asks, the work for a framework comes out as one package: a summary, where each control stands, the evidence on file, and the open items.
Coming soonHelp answering a cyber-insurance questionnaire, from the evidence on file.
Straight answer
Readiness and evidence. Never a certificate.
We don’t certify anyone, and neither does CyberAssure. A SOC 2 report comes from an auditor. A CMMC certification comes from an assessor. HIPAA has no official certificate at all.
What we do is get you ready: the controls in place, the evidence on file, and no surprises when the person with the clipboard arrives. What comes out of CyberAssure is advice and working papers. It isn’t legal, accounting, or insurance advice.
Keep going
Talk to a person
An audit coming, or a customer asking questions?
Book a call. We’ll look at where you stand today and what it would take to be ready.